AI-Driven Cyberattacks Are Surging: What Small Businesses Must Do Now
Artificial intelligence has supercharged cybercrime. Attacks that once took weeks of research now arrive as convincing voice calls, perfect-language emails, and malware that mutates faster than your defenses. For small businesses, the math is brutal: fewer resources, the same targets, and higher stakes. The good news is that a focused, modernized security stack can blunt most AI-enabled threats without enterprise budgets. This article explains why the surge is happening, what the new attack paths look like, and the specific controls, processes, and 30-60-90 day actions that put your organization back on the front foot.
- Why AI has supercharged attacks—and why SMBs are in the crosshairs
- What the new AI-enabled attack paths look like
- Five AI-era controls that punch above their weight
- An SMB-ready detection-and-response stack
- A practical 30-60-90 day plan (with budget guidance)
- Governance, training, and vendor risk—shortcuts that work
- Bottom line
Why AI has supercharged attacks—and why SMBs are in the crosshairs
Generative AI gives adversaries three decisive advantages: speed, scale, and specificity. Models can scrape your website, social feeds, and public filings to craft near-perfect lures. Voice cloning turns a 10-second sample into a CFO “calling from the airport” to approve a wire. Code models help low-skill criminals assemble malware, test it against common antivirus engines, and iterate automatically. Meanwhile, small businesses often rely on legacy tools (email-only MFA, flat networks, periodic backups) that assume attackers are slow and noisy. They aren’t anymore.
“If your MFA is just a text message, assume the attacker can get in.”
Attackers target SMBs because you’re connected (to banks, payroll, suppliers), you hold valuable data (invoices, PII, credentials), and you’re more likely to pay quickly to restore operations. You’re not too small to matter—you’re sized to succeed as a target.
What the new AI-enabled attack paths look like
Here are the most common, fast-growing patterns we see across professional services, retail, construction, healthcare, and local manufacturing. Use these to tune training and controls.
| Attack vector | How AI supercharges it | Red flags | Low‑lift defense |
|---|---|---|---|
| Voice deepfake “CEO/CFO” vishing | Cloned voices + scripts for urgent requests | Off-hours calls; new bank details; secrecy pressure | Call-back verification to known number; dual-approval for payments |
| Spear-phishing email | Perfect grammar; context lifted from your website/LinkedIn | Lookalike domains; odd file types; QR codes | Phishing-resistant MFA; advanced email filtering; DMARC enforcement |
| MFA fatigue & token theft | Automated push-bombing; adversary-in-the-middle kits | Multiple prompts; new device approvals; travel anomalies | FIDO2 hardware keys; number-matching; disable SMS MFA |
| SaaS prompt injection & API abuse | Malicious AI instructions hidden in docs/emails | Automation behaving unexpectedly; mass API calls | Least-privilege API keys; allowlisting; human-in-the-loop for risky automations |
| Ransomware with data theft | Faster lateral movement; tailored extortion messaging | Unusual admin logins; disabled EDR; backup tampering | Immutable backups; EDR with isolation; network segmentation |
Five AI-era controls that punch above their weight
These controls deliver disproportionate protection per dollar and time invested. Most can be rolled out in days and maintained by lean teams or a trusted MSP.
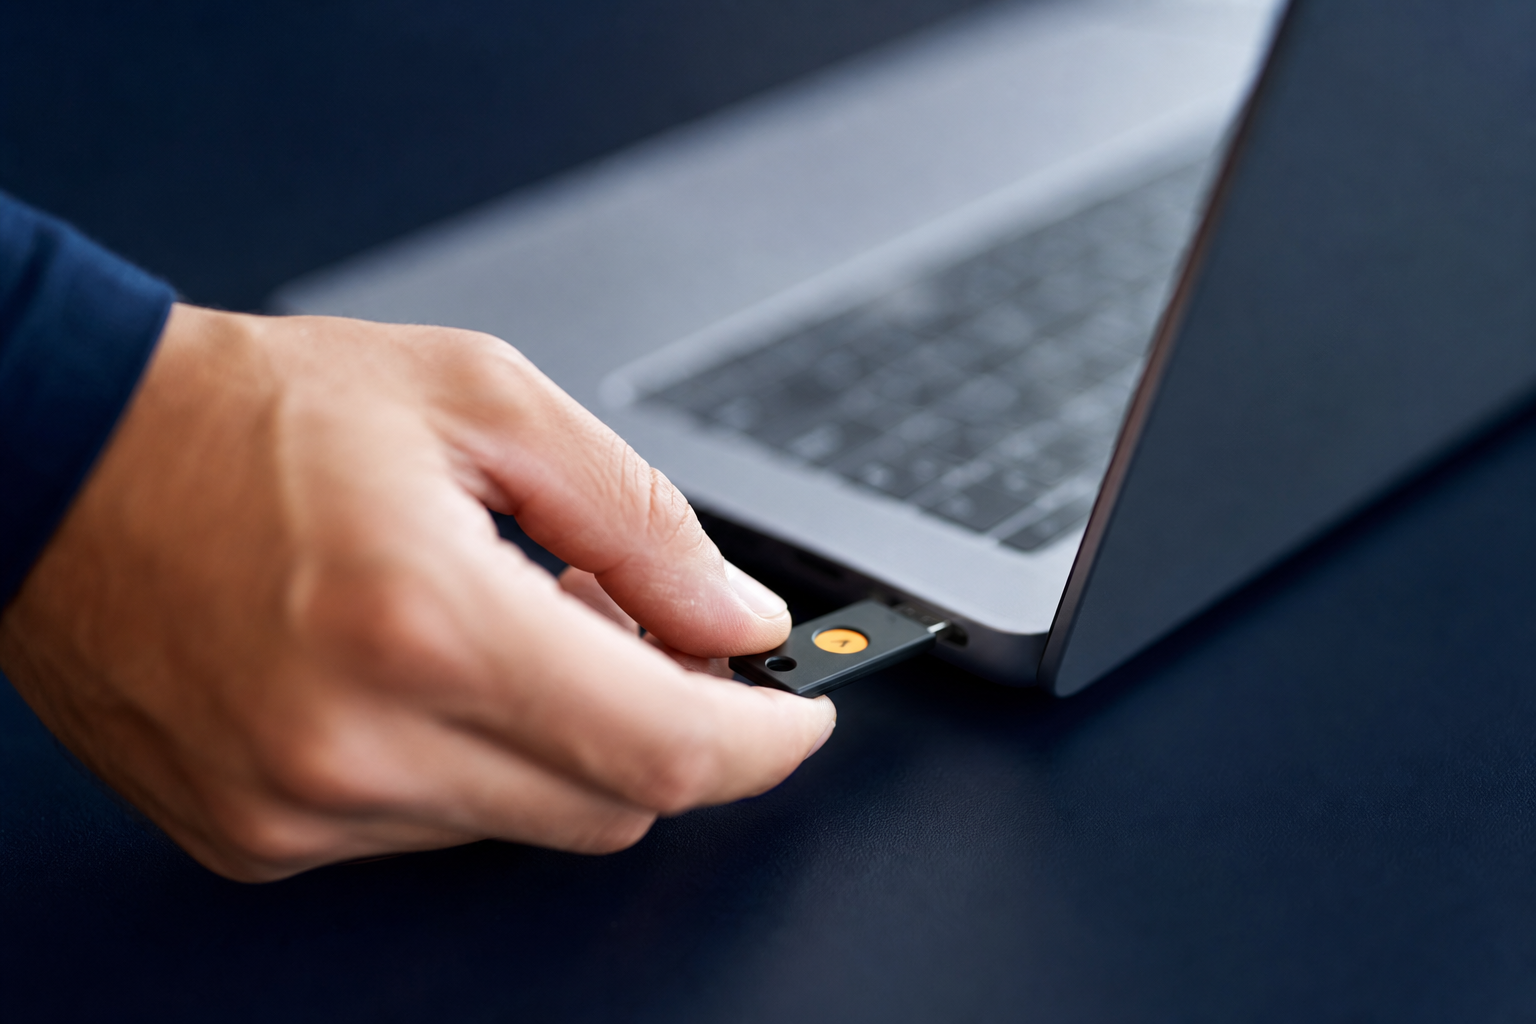
- Phishing-resistant MFA with hardware security keys (FIDO2/passkeys). Push approvals and SMS codes are increasingly bypassed by attacker-in-the-middle kits. Hardware-backed authentication binds login to your device and the legitimate site, cutting off entire classes of phishing and token theft.
- Modern email and domain protection. Enforce SPF, DKIM, and DMARC at “reject.” Add advanced email filtering that scans URLs and attachments in real time, quarantines lookalike domains, and flags supplier invoice changes for human review.
- Endpoint Detection & Response (EDR) with isolation. AI-enabled malware pivots quickly; your tools must, too. EDR should spot behavior (scripted credential dumping, unusual PowerShell) and let you isolate a machine with one click—remotely.
- DNS and application control. Block known-bad domains before payloads land. Add allowlisting for business-critical apps to reduce the blast radius of “unknown” executables and browser extensions.
- Resilient, tested backups. Follow the 3-2-1 rule with at least one immutable or offline copy. Encrypt, separate credentials from production, and rehearse a timed restore so you know how long “back to business” really takes.
An SMB-ready detection-and-response stack
Prevention is necessary but insufficient. You also need eyes-on-glass and automated containment so a single click doesn’t become a week-long outage.
- 24/7 managed detection and response (MDR). Outsource continuous monitoring of endpoints, identity, email, and cloud/SaaS. Ensure your MDR can quarantine endpoints, disable accounts, and block domains without waiting for your approval in obvious emergencies.
- Identity threat detection. Turn on conditional access, impossible-travel alerts, and risky-sign-in policies. Feed logs from SSO, directory, and key SaaS apps into a central alerting channel.
- Network containment. Use microsegmentation or at least VLANs to separate finance, point-of-sale, and guest networks. Adopt a small, managed security appliance that can enforce DNS filtering and block command-and-control traffic.
- Playbooks with role clarity. Who can approve shutting down remote desktop? Who calls the bank? Who notifies customers? Store contacts outside email (in case accounts are compromised).
A practical 30-60-90 day plan (with budget guidance)
Use this time-boxed plan to reduce risk fast. Adapt the budget bands to your size (fewer than 50 employees vs. 50–250). Costs assume you already license a mainstream productivity suite.
Days 0–30: Stop the bleeding (focus: identity, email, backups)
- Turn off SMS MFA and require number-matching prompts and/or FIDO2 keys for admins and finance first; roll to all staff in phases.
- Set DMARC to “quarantine” then “reject.” Align SPF/DKIM, lock down external forwarding, and add supplier-impersonation rules.
- Deploy EDR across all endpoints; baseline your environment and enable automated isolation.
- Backups: create an immutable copy, rotate backup credentials, and perform a timed restore test for one critical system.
- Train for voice deepfakes: implement “call-back to known number” and dual-approval for any bank detail changes or wires.
- Budget band: $0–$2,500 one-time (keys, configuration), plus monthly MDR if selected.
Days 31–60: Contain and detect (focus: network, SaaS, playbooks)
- Segment networks: separate guest/IoT/point-of-sale from business traffic; enforce DNS filtering.
- Harden SaaS: least-privilege roles, API keys scoped to tasks, disable legacy authentication, and monitor OAuth app grants.
- Choose MDR/SOC partner or expand your MSP scope to include 24/7 alerting and response authority for clear-cut events.
- Write three one-page playbooks: “BEC/wire fraud,” “ransomware,” and “account takeover”—with names, numbers, and go/no-go thresholds.
- Budget band: Additional $1,000–$2,500 setup; MDR/EDR typically $10–$40 per user/month depending on coverage.
Days 61–90: Prove resilience (focus: testing and recovery)
- Tabletop exercises: run a 60-minute scenario for each playbook with your leadership and MSP.
- Restore rehearsal: recover a production-like system from backups to a clean environment; document time-to-recover and gaps.
- Close findings: convert issues to tickets with owners and deadlines; measure mean-time-to-detect and mean-time-to-contain.
- Budget band: Mostly time; optionally invest in backup immutability or microsegmentation if you deferred earlier.
Governance, training, and vendor risk—shortcuts that work
- Policy, but keep it human: a one-page “AI & Automation Use” policy that bans pasting confidential data into public tools, requires human review for payment-related automations, and documents approved AI tools.
- Least privilege everywhere: admin roles only for those who need them; break-glass accounts stored offline; require SSO and MFA for all business apps.
- Vendor due diligence, right-sized: ask for evidence of security controls (encryption, SSO, role-based access, backups). For critical vendors, require breach notification within 72 hours and confirm how you’ll retrieve data if you exit.
- Realistic training: simulate AI-written phishing and voice deepfakes; teach staff to “trust but verify” via call-back to known numbers and out-of-band checks.
- Public resources: Bookmark and use templates and alerts from cisa.gov, nist.gov, and small-business guidance from ftc.gov.
Bottom line
AI has tilted the field toward attackers—but it also lets lean teams defend smarter. A small set of modern controls (phishing-resistant MFA, EDR, DNS filtering, segmentation, and immutable backups) combined with 24/7 monitoring and crisp playbooks will stop most real-world incidents before they become business-ending events. The key is sequence and speed: secure identity first, then email and endpoints, then networks and recovery. If you commit to the 30-60-90 plan, you’ll materially reduce risk, improve your recovery readiness, and regain the confidence to keep innovating without fear.
Ready to explore how you can streamline your processes? Reach out to A.I. Solutions today for expert guidance and tailored strategies.